Are You Ready to Witness the Future of Data Security?
Platform
Resources
©2026 QuNu Labs Private Limited, All Rights Reserved.
TL;DR
Every so often, a security event resets the baseline. After it, the assumptions you held the week before no longer hold. October 2026 was one of those events.
Researchers are calling it Black October. Over roughly 72 hours in the third week of the month, serious incidents landed at once: a flaw in the software behind most of the web, the collapse of trust in a major certificate authority, customer records from India’s largest bank on the dark web, poisoned developer tools, and banks locking autonomous AI agents out of customer accounts.
Any one would headline a normal year. They arrived together. Strip away the noise and most point at the same weakness: the cryptographic trust the internet runs on is more fragile than we treat it. This is a before-and-after moment for digital trust, and a small preview of a larger problem now two to three years out.
Black October is less one attack than a pile-up of disclosures, several building for months before going public between October 19 and 22.
Underneath all of it was AI. AI even found the flaw at the center of the week: the PHP vulnerabilities were uncovered by AI tooling, which the security firm Wiz called the most severe vulnerabilities the technology has yet discovered. The same autonomous agents that help developers automate real work also let attackers scan, probe and exploit at machine speed, around the clock. In the same week, JPMorgan Chase said it blocks external AI agents from operating inside retail customer accounts, with Charles Schwab and Citigroup setting similar limits, citing the risk of rogue agents.
Look at what actually broke. A certificate authority vouches for identity online: when your browser trusts a bank’s site, it trusts a chain that ends at a certificate authority. eMudhra is one of those authorities, with more than 60 million certificates issued.
Its private keys were meant to be enormous, effectively un-guessable numbers. Instead, a faulty script during an April 2025 key-generation ceremony produced keys so weak that researchers recovered them from public data in under a second. One was the number 4. No attacker broke the math. The keys were never strong.
This is the point most coverage misses. The failure was not exotic. It was randomness. A key is only as trustworthy as the unpredictability behind it. When the randomness is weak, the key is guessable, and everything built on it, every certificate and encrypted session, is open.
The shift is not theoretical, and the attackers are ahead of most defenders. In October 2026, Kaspersky detailed Operation FlashHole, a campaign it attributes to North Korea’s Lazarus Group that targets South Korean organizations through a complex infection chain. The group’s LPEClient malware now pulls ML-KEM-1024 public keys from its command server and uses them to protect later-stage payloads. ML-KEM-1024 is the NIST-standardized post-quantum algorithm.
Read that again: A state-backed attacker adopted post-quantum cryptography to secure its own operation before most enterprises have migrated to secure theirs.
What Quantum-Safe Security Actually Requires
As QNu Labs CEO Sunil Gupta puts it: “Security is not a cure you reach for after the disease. It is an immune system, built before the infection, never after.”
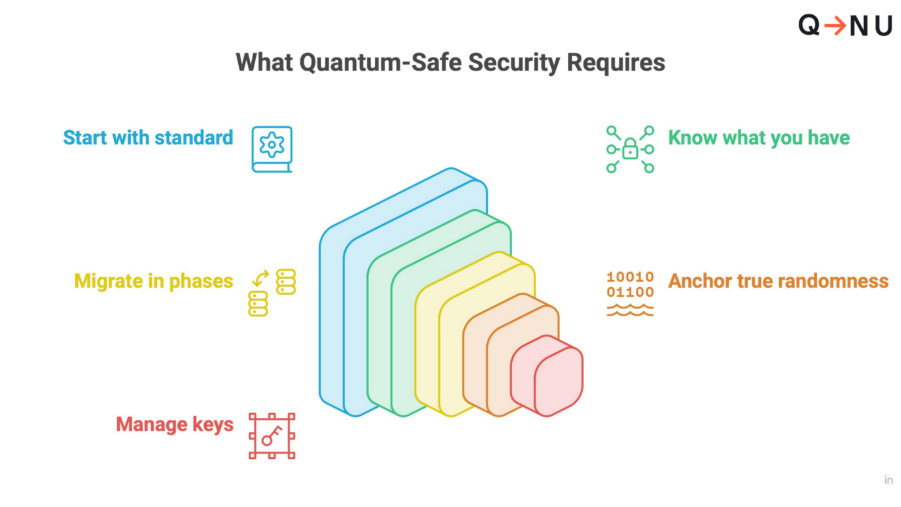
The response to Black October, and to the quantum threat, is a sequence, not a scramble:
The most exposed sectors, such as banking, finance and insurance, sit at the front of the line.
QNu Labs is a full-stack quantum security company, built in India and fully indigenous. Its QShield platform spans hardware, cryptographic and application layers: QKD (quantum key distribution) and QRNG hardware, NIST-compliant PQC, and quantum-safe VPN, messaging, storage and key management.
In April 2026, under the National Quantum Mission, QNu demonstrated India’s first 1,000 km inter-city quantum key distribution network using indigenous technology, one of the longest such deployments in the world. It holds India’s largest quantum-security patent portfolio, with 12 granted patents and 15 pending, and is backed by the National Quantum Mission.
Black October will fade from the headlines. The weakness it exposed will not. The practical move is not panic: adopt the standard, map your exposure, migrate with room to adapt, and anchor every key in randomness that cannot be guessed.
Explore Quantum Random Number Generation to see how true randomness becomes your root of trust, or Request a Demo to map your quantum-safe migration.
Sources: